
Hello, Lately my company is having some issues with some users that have a common problem. The problem is that the FMC is seeing identities as the wrong users, users who aren't actually logged onto the computers (Windows 10). ISE logs show the correc...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(10) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,338) -
Cisco Bugs
(65) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(282) -
Cisco Secure Firewall Threat Defense (FTD)
(341) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(21) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(27) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(39) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(88) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Open Source and Open Standards
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Automation Analytics Topics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other IP Telephony
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(28) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Is there any plan to support ASDM on Windows server 2016 OS?
Resolved! FMC / FTD Management IP/FQDN Problem
We just changed a Module SM-56 on a Chassis 9300. Everything works great, only that now on the FMC the Device has now an IP instead of FQDN under management. All other Modules, and Devices are using FQDN for the Management Address, and it was working...
Hi Experts,I hope everyone is doing fine and well. I have this problem with my FTD for more than a month already. I will start this out with what happened at first.I have a ASA5508X hardware running on FTD7.0.6 with FMC 7.3.1.End of September we inst...


Hi dears,when entered the switch to universal P L R from F D M (Firepower Device Manager) , and copy the request code to smart license reservation, appears error as shown the attached image. how to enable !!
Good Morning all, I am working on a new network deployment and at the top is a Cisco Firepower 1120. I am going down to two datacore switches from the firepower and would like each datacore switch to have it's own uplink from the Firepower. Each in...
Hi everone ASA5510 can't connect ASDM and http port 443 and i know ASA 5510 EOL I use command "show run all ssl" command show "ssl encryption rc4-md5 des-sha1 3des-sha1"how to reslove problam? thankyou
HelloI have been trying to access my FPR 2100 firewall for around a week but without success.Before the problem occurred I freely connected to the port management and typed the address 192.168.45.45 in the browser to access the device manager web int...
Resolved! Cisco ASA1120 Active/Standby Failover
Hello,I am currently configuring two Cisco ASA 1120s for Active/Standby failover. So far it is failing. This is what I have done so far. The version that these ASAs are running is Cisco Adaptive Security Appliance Software Version 9.16(4)42. They als...
Hello Team,Is it possible to filter VPN remote access with mac-addresses as a second layer factor security in addition to username/password on FMC?If yes, any ideas to approach this?Thanks.
Resolved! FTD Module FPR9K-SM-56 Faulty DIMM / RAM
We are having a Faulty SM-56 (in a Firepower 9300)slot/1/fault/F1546Description:Security Module 1 is in failed state. Error: Security module is downgraded (or) not acknowledged. Reason: DIMM or CPU degradedWe even know which DIMM is bad: Memory Array...
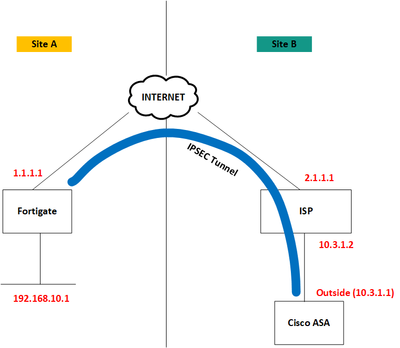
Hello, I have built an IPSEC site to site VPN tunnel from one of our Cisco ASA to Fortigate firewall. The tunnel is up and running and traffic is passing though the tunnel as expected. Now I have a requirement to track the tunnel status via SLA monit...
Hey everyone! I have a weird situation going on with my failover and I just wanted to make sure the best practice for the HA Pair of a FTD. I have two outside interfaces with the same IP and I think when they have the same IP it broke the HA pair. Q...
Firepower 1010 (ASA-Image): ASDM does not work anymore after upgrade Hello everybody, I upgraded the Firepower 1010 (ASA-Image) from 9.14(4) auf 9.18(3)56using the ASDM and the upgrade worked without issues. Directly after the upgrade I still could o...
Hi,We used the migration tool to move from ASA5525s to FPR3110s and the tool appended "no-lookup" to most of the rules but not all. If anyone knows what this designation implies, as well as it's absence, I would greatly appreciate knowing. Thanks.
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 4 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


