Network Security

Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
cancel
Showing results for 
Search instead for 
Did you mean: 
cancel

“Join

 
Labels

Forum Posts

Hello, I would like to know the meaning of these words (P0/P2) in an ASA capture: CISCOASA# capture TOTO interface Guest real-time4: 11:04:48.898055 802.1Q vlan#XXXX P2 172.22.X.X.50336 > X.X.X.X.53: udp 395: 11:04:48.908034 802.1Q vlan#XXXX P0 172.2...
reno51 by Visitor
  • 4878 Views
  • 3 replies
  • 0 Helpful votes

Earlier this year, we purchased some ASAv virtual appliances with an SWSS service contract.  The service contract lists the instance number in place of the serial number on CCW-R.  The serial numbers on the VMs are not associated with a Service Contr...

I have two identical ASA 5585 working in Active/Active. On Primary Unit i want to changefailover group 1  secondaryfailover group 2  preempttofailover group 1  primaryfailover group 2  primary After configuring this change;spyker/pri/act# conf tspyke...

Hi ,I would like to ask about reverse flows error. I saw the same issue in forum and try to fix. But May be i don't know how to add NAT Exemption rule or my exemption rule is doesn't work.vSo please help me to fix.My network information :inside-net=2...

MrBeginner by Spotlight
  • 10632 Views
  • 13 replies
  • 0 Helpful votes

Hi folks, I have a customer who owns a FPR4140-NGFW-K9 with just the factory 8 port 10GB network module.Due to budget constraints, they want to upgrade with an additional 1 GB 8 port module and move some cables over from the original.Can be the HA po...

Jorge F by Frequent Visitor
  • 2117 Views
  • 2 replies
  • 0 Helpful votes

Hello, I am not able to use the user name and password created by a sponsor in Cisco ISE.Also before i log in i can still access the internet but i cant access ISE.  Please help.

Tutu by Level 3
  • 4427 Views
  • 8 replies
  • 0 Helpful votes

I'm running 6.6.0-90 on a FPR1120 in FDM mode. Whether or not I use the default NTP servers or enter my own, the unit will not sync up. When I run 'show ntp' the status of each server (including 127.127.1.1) shows unknown. From the CLI console, I als...

Baryon324 by Visitor
  • 5849 Views
  • 12 replies
  • 0 Helpful votes

Hi, We took over a system that didnt keep the greatest of notes on the system. I'm in a situation where we don't know the Tunnel group key or the Failover key. Is there any way to get these keys without taking the system down? Thanks for any help!

K-Grev by Level 4
  • 1901 Views
  • 2 replies
  • 0 Helpful votes

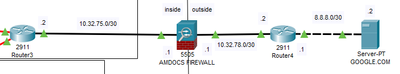
Hi everyone, im trying to find out how to specifically permit source ip going to destination. Im using Packet Tracer. It is working when I use this command,access-list 100 extended permit tcp any anyaccess-list 100 extended permit icmp any anyaccess-...

image.PNG
carloade by Visitor
  • 3902 Views
  • 10 replies
  • 0 Helpful votes

Hi all   I have FTD 2130 version 6.2.3.2 , I'm facing that server trace e.g. 8.8.8.8 always show * I had read many articles , I had  tried   1. set policy from outside to inside allow icmp all 2. add flexconfig with      policy-map global_policy     ...

peter0023 by Community Member
  • 12621 Views
  • 17 replies
  • 0 Helpful votes
Review Cisco Networking for a $25 gift card
