
Configured IP sec but when this Comamnd sh isakmp sa get the output There are no IKEv1 SAs sh run access-list outside_cryptomap extended permit ip 172.16.8.0 255.255.248.0 object NETWORK_OBJ_192.168.12.0_22nat (inside,outside) source static NETWORK_O...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,337) -
Cisco Bugs
(63) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(281) -
Cisco Secure Firewall Threat Defense (FTD)
(340) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
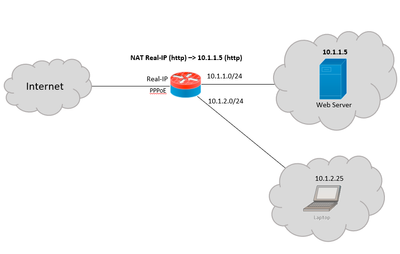
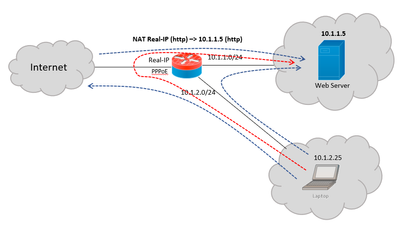
Let’s imagine very simple configuration: Internet -- Cisco ASA -- two internal networks (one for users one for Webserver)Webserver is accessible from internet over a static NAT rule:object network Server-httphost 10.1.1.5nat (inside,outside) static i...
I have the problem that i can not connect with my web server in DMZ network6Apr 12 201916:58:4930201462.245.164.71443172.16.0.257288Teardown TCP connection 1427 for outside:62.245.164.71/443 to DMZ:172.16.0.2/57288 duration 0:00:05 bytes 56148 TCP FI...
Hi, I'm trying to understand the qos maps on Catalyst 2960x in order to implement on my network for voice application.I've set the dcsp value to 46 for the voice application in Windows with group policy to prioritize the voice traffic along with traf...
Hi all,I think i have a very simple case. Consider the following topology:Yesterday i did a ping sweep with nmap from our AnyConnect VPN. Our internet facing firewall (where AnyConnect VPN is running) was logically reporting a TCP SYN attack and a lo...

Hi, I have a Firepower 7010 with no power lead. What type of power cable do I need to search for online? I searched the data sheets on cisco.com, but the power cord stipulated is not correct (IEC C13/14). I have attached a picture of the interface ...

What is the best way to move malware policies tied to our existing 5525 to a Firepower 2120? In the FMC, do I apply the rules to the ACP used by the new FTD appliance?
Hi, I am running FMC 6.2.3.4 which can reach internet but it is unable to show public AMP Cloud (US, EU and APJC) in FMC GUI(AMP-> AMP Management). It shown None as AMP Cloud. Please help me to sort it out. Thanks.
Resolved! Firewall rule name in logs
Regarding Cisco ASA: Can I configure the ASA to include the firewall rule name in each log entry ?Can I put any name in the rule, is there some character restrictions (as comma) ?My aim is to include tags in rule names to filter the logs before they ...
My configurations was working with Site to Site VPN with IKEv1 using PSK. I created certificates and the connections are working. I can see some good debugging on the other side because it is Strongswan on a linux host. I shows everything is con...
%ASA-6-302015: Built outbound UDP connection xxxxxxxxx for outside:xx.xx.xx.xx/443 (xx.xx.xx.xx/443) to inside:xx.xx.xx.xx/57916 (xx.xx.xx.xx/57916)In which condition UDP connection is established for destination port 443?
Resolved! ASA OS Upgrade
Hello, I am perplexed by the way ASA OS releases codes are structured. We have purchased several Firepower 2110s which came pre-loaded with release code 9.8.3. I opened a TAC case to inquire about the recommended release code and the response I re...
Firepower gurus: Looking for input on two questions I received from a Firepower sys admin: Is there a way to block ALL uploads in one line? Does this capability exist? Does a website or application that other Firepower users have posted combinatio...
Hi all, I got error message "You do not have sufficient privileges to execute commands required to load ASDM. Please contact your system Administrator". Do you have any suggestion?
HiGood day to you I need your advice regarding FTD clustering in firepower 9300 let me explain what the customer is asking for • We have two FP9300 chassis and every chassis has two FTD security module SM-44• The customer want to deploy it as a clust...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 6 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


