
Resolved! Categories list from FMC
Hi Community Team Does anyone know, if it is possible to get the Categories and apps list from FMC?, is avaiable to download or copy in somewhere or from FMC? I can't copy them directly Thanks

Hi Community Team Does anyone know, if it is possible to get the Categories and apps list from FMC?, is avaiable to download or copy in somewhere or from FMC? I can't copy them directly Thanks
I have an ASA 5516 that is having intermittent issues so is being swapped over. I have taken a backup of the main ASA via ADSM and have restored onto the replacement device.I was just expecting to be able to just swap over the ASAs and reboot the swi...
Dear allI have a quick question for Firepower 1010 ASA firewall: Does the outside interface E1/1 support VLSM IP address? They want to assign a static IPv4 address with /22 netmask (255.255.252.0) on Ethernet 1/1 (outside interface).I can’t find the...
Hi GuysLAN (inside) network - 192.168.10.0/24WAN (outside)network - for eg 137.14.191.12/28Device: Cisco Firepower 2100 series managed by vFMC I have around 15 servers residing inside the campus that needs to be opened for public. Each server has dif...
Hi, We have two Firepower 4110 units that only have 2 logical interfaces. One is from a Gigamon tap and configured as a passive interfaces and the other is the management interface. We are using these units essentially as out of band IDS units. They ...
Dear All, Please, I need guidelines on how to configure inspection policy for access rule on ASA Firepower for inbound traffic.Currently, I have 3 policies configured as following1. default policy2. Policy for outbound traffics inspection which worki...
I have Firepower 8000 Devices at Core Layer of my network. Code version for these Devices are 6.3.0.1. FMC for this device managed from is 6.4.0.4. Does Firepower 8000 support FQDN Objects ? if yes can you provide reference to it ? and tested it ?
Hi guys, I'm running a firepoower 2100 with asa image 9.12.2. An interface of the firewall is connected to production network in a uncontrolled space. For this reason I was trying to check some sort of network attack on that interface to double check...
Hello Cisco Community I have configured the above firewall using Firepower Device Manager , i am a bit new to this GUI interface, and i am having issues with the access control. I have set up all my objects with their appropriate IP addresses and hav...
My understanding is the syslog is based on the "Real-Time Log view which has the columns "Severity", "Date - Month, Year(Year to be remove)", "Time", "Syslog ID", "Source IP", "Destination IP", "Destination Port" and " Description" How can I remove f...
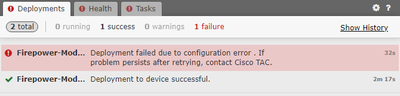
Dear Community i'm facing the following error when i deploy the Access Control policyone of the 5525x firepower succeed while the other fail.the FMC is a virtual appliance.even when i deploy a basic any to any policy
we have an ASA 5500x environment like this.Main site 5516xremote sites 5508 and 5506x we are using a Firepower Service VM to manage all the firepower services on the devices.we are not in FTD mode. since the 5506x w/firepower is now EOL, is it possib...
Hi, I have enabled DPI inspection on my FTD units. When I whitelist a URL by domain or URL, via the connection events in the fmc, I am still getting blocked for the URL category. Per the event log, it is getting de-crypt and the behavior is same with...
Dears,Happy new year to all; I have an issue regarding retrieving web content for web service from my webvpn (clientless-ssl ), please advise me regarding this issue as attached. ASA Model: 5515Version: 9.12 Thanks.
I am trying to send a POST request to the Firepower REST API. See the following information:POST accesspoliciesRequest Type: POSTDescription: Creates an access control policy with the specified parameters.URL: /api/fmc_config/v1/domain/{domain_UUID}/...
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |



