
Hi Has anybody done Migration from vFMC to FMC Appliance? Thanks
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,338) -
Cisco Bugs
(63) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(282) -
Cisco Secure Firewall Threat Defense (FTD)
(340) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Hi all! I'm trying to understand why the keyword "default" in the ACL is needed. R3(config-ext-nacl)#? Ext Access List configuration commands: <1-2147483647> Sequence Number default Set a command to its defaults deny Specify packets to reject permi...
Dear All, Please guide me on below query Server 10.1.1.1 | | dmz R3-----outside----ASA-inside--------PC-B Internet | ...
Hello, I have a site-to-site VPN between two remote sites which is working as expected. LAN subnets at both sites are allowed for access over the VPN. I would like to be able to access the remote site when connecting remotely via AnyConnect to the lo...
I have a FP2110- 6.2.2 with 2 sub-interfaces (vlan11 and vlan99) on physical interface 2. I have a C9300 connected trunked to the FP and have a 2 laptops connected to switch ports that are assigned to the vlan 11 and vlan 99. FTD vlan 99 - 192.168....
hello, I have 3 interfaces configured on my asa version 9 (inside1, inside2, outside) I can reach internet from the two interfaces, but i can't reach the inside2 interface from the inside 1 interface I have this error in the asdm logs "Fail...
I currently have a deny rule for one of my interfaces. When selecting this rule in the asdm and selecting logging the window pops up with the filter selected for this rule. The issue is that not all the deny hits are showing up in the logging window....
Hi All I am having issues bringing up a vpn between an ASA and a Checkpoint firewall. I am using the normal settings that we use to connect on our others but this one fails to come up. I can see all the phase 1 proposals sent through, approx 10 sets,...
Resolved! Active directory Realm error in FMC log.
I'm getting the following errors in the FMC syslog. I'm not sure this is causing any issue as we are currently in the progress of standing up our firepower implementation and don't have any access policy using any user criteria yet. I just want to ...
Hi guys, I am planning to upgrade my FMC which is deployed in HA mode. Just thought because based on the process, I need to pause the sync of 2 FMC, do I need to upload the upgrade image to both FMC nodes or uploading in the Active FMC before pausing...
Hi guys, I need your input about this design scenario. I want to break current 3850 stack into 2x 3850 separate units and add HSRP between them. On each ASA failover pair I will monitor interfaces connected to the HSRP switches. Routing wise I am u...
Hi everyone.I have a problem: 2 asa 5512-x in failover and dualwan mode. 5512 has 15 IPSec tunnels are configured with asa 5505 and 1 with routerboard(mikrotik) for testing. Software version on 5512x asa912-smp-k8.bin, and 5505 asa901-k8.bin. There i...
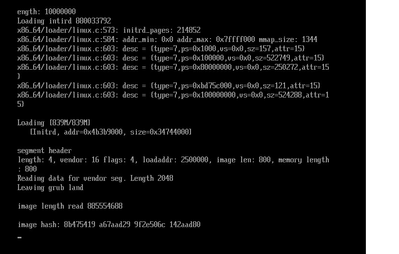
Hi; I deployed NXOSv ova image (nxosv-final.7.0.3.I7.2.ova) on ESXi 6.5 and decreased RAM from 8G to 5G and CPUs from 4 to 2. Then started VM but it stuck at the following page and doesn't do anything. Any idea? tnx.
Resolved! Categories and URL content list
Is there a place you can actually find out what URLs are contained within each category item? It would be nice to be able to look up to see what URLs a particularly category contains.
Respected All, As of Now "Dual AAA Authentication" no supported in FMC 6.2.3 for FTD 2100 Series. But we want that by Third Part Tools. Third Party asking us to integrate their RADIUS with Cisco FMC 6.2.3 (FTD2120). Post Integrating Authent...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 6 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


