
I have two Cisco Firepower 2110 in HA Configuration. I tried to perform version upgrade from 6.4. to 6.6. I got Device2 (Standbyd device) upgraded to 6.6. But the Device1 (Primary) failed the update. And the Device1 i showing up in maintenance mode a...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,337) -
Cisco Bugs
(63) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(282) -
Cisco Secure Firewall Threat Defense (FTD)
(340) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Hi there, I got a Cisco vFMC with two Cisco Firepower configured as HA pair. At present the Secondary unit is Active. We got an issue with the Primary unit and have to perform factory-reset. I got a couple of questions: 1) Do I have to break the HA ...
Which version of IOS patches this advisory?Cisco IOS XE Software for Catalyst 9000 Family Wireless Controllers CAPWAP Remote Code Execution Vulnerability I can't find any IOS XE version released around the date of the advisory. The newest version I ...
We have two ASA 5525Xs who's management interface is on our OOB management network (172.16.8.0/22). Until now, the ASAs were sending SNMP (for port traffic) and NetFlow traffic to a server (172.16.4.45) on one the ASAs standard interfaces (172.16.4.0...
HelloI created a site to site tunnel. The vpn is up but the truffic does not pass. Attached the logs found.Cordially
Resolved! Network Link Encryption
Hi all, hope to find everyone well in this timesI had a request from a costumer where he said that I need to have all the network links encrypted but I have no clue how to implement this.Basically the core of the network is comprised by Cisco 9300L i...
Resolved! Two default routes in FTD-2130
Hello guys, I'm using FTD-2130 version 6.3.0 managed by FMC version 6.5.0, how can we use two default routes to the Internet ...
Hi All, I am working with a very peculiar design requirements, where we are using FMC4500 and FTD 4140 with container instances. We have assigned a Eth1/8 interface as logical management interface to be shared by all containers. Now the requirement i...
Resolved! SAML Redundancy for Cisco ASA
Hi Everyone, I have customer who has an ASA in Active/Standby mode and have SAML Single-Sign-On configured. The SAML SSO works fine but during failover, it gave and error "Authentication failed due to problem retrieving the single sign-on cookie. ...
Hello, Zone Based Firewall is dropping packets from one interface to another and I cannot understand why.1) There is a zone-pair between both interfaces2) All IP traffic is allowed3) In the log says (target:class) - (none:none). Not event class-defau...
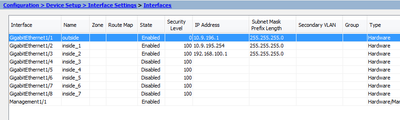
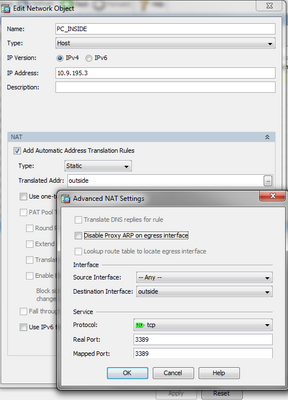
Hello, I am facing a problem to have RDP port forward to a PC inside the firewall on ASA-5506-X. ASA version 9.8.Ethernet port 1 configured as ouside, ethernet port 2 configure as inside_1, ethernet port 3 as inside_2. other enthernet ports are disab...


Resolved! Monitoring FPR 1120 by FDM
Hi team! I currently have an FPR 1120 which I manage from my FDM. The version of Threat Defense used is 6.4.0 102. I require network management much like ASDM does with ASAs. With URL filtering, network throughput management, etc. Is this possible w...
Resolved! ASA 5585-X 10GE license
hello I have two ASA 5585-X in an Active/Standby failover.I tried to install the 10GE license on both units. I am getting the below error. SHZF-DBFW-5585X-01# activation-key d81ace61 1838c7b5 7870a944 85949800 c73b0680Validating activation key. ...
Resolved! Firepower (FTD) HA designs
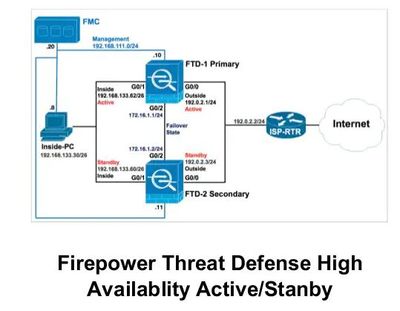
We are looking to get 2 new FTD's and want to deploy them in a HA pair, I've been going thru docs and designs and noticed all of them show a RTR as the edge device and both FTD's coming off of that. (with private ip addresses on the outside interface...
Resolved! allow webvpn access from 1 IP address
Good Day,I would like to lock my ASA-5506 down to allow WebVPN access only from the remote office. I am thinking I need to apply an access-list to the external interface?webvpnenable outside permit 8.8.8.8 255.255.255.252 <-- used google dns as an ...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 6 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


