
Hi , I'm configuring FTD HA managed by FMC.I was confused with Monitored Interface configuration when configuring FTD HA. I've outside interface going to router an inside interface connected to switch.If I put standby IP address for monitored interfa...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(10) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,335) -
Cisco Bugs
(60) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(139) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(55) -
Cisco Secure Firewall Management Center (FMC)
(275) -
Cisco Secure Firewall Threat Defense (FTD)
(329) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(21) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(27) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(88) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,234) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Open Source and Open Standards
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Automation Analytics Topics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other IP Telephony
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,660) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(28) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Resolved! 6.6.1 to 6.7 Upgrade Stuck
Hello All,So yeah, here is what the log is showing and it's been almost 24 hours, TAC is still investigating and this sucks. Any ideas and how can I stop/fix this. I'll update my post here as soon as I find a solution but I would like to see if anyon...
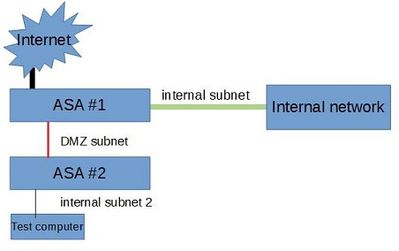
I have an odd situation involving two ASA firewalls that I'm trying to configure to allow traffic to-and-from both the outside world and our main private network to reach the private network of the 2nd firewall.I have no problems getting the traffic ...
Hi all, I'm trying to setup a IOS(-XE) based ZFB-firewall to filter and block traffic between 2 LAN-segments. I have a list of ports which I want to allow but I find it hard to find an example to match a port in a class map if the port does not match...
I have a pair of 5555-X ASA running 9.3(1) that I plan to upgrade to the version 9.14(1.30). I am planning this as an outage to services that traverse the firewall but am wondering what the true impact will be. Since I have two in an HA pair (activ...
Hi, There would a way to find out SFP serial number for out of band interface. I got Please serial number for ethernet ports and slots. But i did not find serial number of SFP for out of band interface.Model - 4125I have used below commandftd/fabric-...
Resolved! Factory reset
I have two Firepower 1140 with FMCv. I have been running these in my lab environment. I want to move these to production but before I do I want start with a fresh config. I have been trying to figure out how to do this. I don't see a way to clea...
Hi I develop rule register automation application by using rest api. I would like to know rule hit-count and if it possible, last hit date. Surely, I know how to find hit-count via CLI. (show access-list) But I could not find this in rest a...
Resolved! Transfer Cisco Firepower License
Hello.. i have a cisco 2110 FTD with TMC License , there is any way to transfer this license to Firepower Virtual
i have configured cisco asa 5520, i am here to ask about one possibility according to my needs. i have two internet connections. both are configured in cisco asa as internet. for example. 1st link = 1.2.3.42nd link = 5.6.7.8 is it possible i can conf...
Hi, We updated our FMC virtual appliance from 6.4.0.9 to 6.6.1. It has the required 32GB RAM and 4 vCPU. Since the update the CPU Usage health test in FMC Health Monitor reports as 'Test Failed'. Has anyone encountered this issue? Regards,PW
Anyway to provide Anyconnect users static IP from ASA, other than DHCP pool IP.Architecture is Anyconnect <> DC ASA <> DC ISE <> Corp AD Anyconnect users are corporate AD users. ASA sends requests to ISE and inturn to AD. ISE does some posturing chec...
for example 192.168.1.1, 1.2 and 1.3 in /24 subnet
Hi All, am facing some basic issue with ASA Nat on EVE-NG . I am not able to ping after using below mentioned nat statements, but I removed these NAT statements am able to ping ( Dst 10.10.44.100) from Src 192.168.20.100. But at same time NAT Tran...
Hi there,i have cisco ASA, i have configured it for redundant or backup isp links, but when one link is down its not shifting to the backup link please help me does this asa 5520 support this feature or not please also tell me that.
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-24-2026 02:14 AM | ||
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |


