
Do we have any command to list out the high-performance snort rules the way we have for low performance? Also commands for what all protocols are consuming the high performance.
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,338) -
Cisco Bugs
(65) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(287) -
Cisco Secure Firewall Threat Defense (FTD)
(343) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(39) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
I have ASA 5525X, on my NMS showing high utilization of mempool_global_shared as shown in the attachment. Is it normal, any reference link from Cisco as not to monitor this object?
I have a application behind Cisco ASA & the application uses UDP.The client connects to the application using UDP port & there is 2 ASA firewall between the client & the application server. ASA 1 does the source NATASA 2 does the destination NAT Let ...
Hello, I have created a VLAN and I want limited traffic going between the VLAN and my inside interface. I have traffic moving from the VLAN to the 2 IPs on the inside. However I cannot access the VLAN from the inside interface. Here is my config. Can...
Hi Experts,We've ASA with Sourcefire module installed and I've queries on Network Discovery. Please excuse my lack of skills on Sourcefire as i'm new to this. On going through the videos, noticed Network Discovery is the initial step is learning the ...
I have FTD virtual 6.4 managed locally ( FDM ) , does it support anyconnect if I want to get a temporary license to test ?
Resolved! Reduced number of AnyConnect sessions
Hi, We purchased a pair of ASAv50 for a failover setup. I noticed that the number of AnyConnect sessions is reduced to 750 even if we have enough licenses and the platform is supposed to support up to 10000. Why does this happen? License mode: Smart ...
We have a newly deployed FMC 2500 hardware appliance that we are staging in preparation to be added to our production network....it was authenticating via RADIUS to our ISE VM node....our ISE node crashed and has to be completely rebuilt and in the ...
Hi,I have ASA 5525-x and i wanted to use the IPS Software module (Whichi never used it before). Can you please help me to configure the IPS Module.Below is the output of Sh Module IPS

I've setup a new FirePower 2130 and I want to monitor the interface usage of it. I'm using Eth1/1-Eth1/4 of the device and they are configured and up Interface: Port Name Port Type Admin State Oper State State Reason -------------- ------------------...
Resolved! FMC not booting
Hi experts I have an issue with FMC.Its not coming up.Attached screen shots.Please Help
Resolved! ASA 5516-x ASDM don't connect firepower.
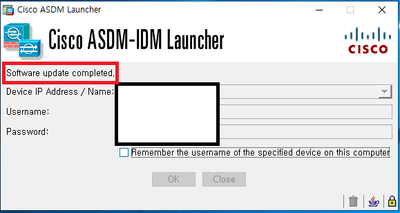
Hello.My ASA 5516-x don't connect firepower.I launched asdm, asdm is stucked "software completed" about 1-2 mins.after 1-2mins, asdm boot up, but I can't see firepower panels.and I clicked "ASA firepower Status", ASDM is stucked constantly, so i need...

I am trying to change the syslog port number from udp/514 to udp/5141. However when I look at the traffic it appears to still be sent on udp/514 logging enablelogging trap informationallogging asdm debugginglogging host inside 192.168.55.225 17/5141
Resolved! Accessing ASDM from Anyconnect VPN
hi,i want to access the asdm when connecting through any connect vpn, when i connect through anyconnect, i get an ip from a pool of 172.50.50.0,i added this to my ASA config:http 172.50.50.0 255.255.255.0 Insidebut still i cant access the asdm, is th...
Hi Experts,I'm migrating 5525-X HA to 5555-X HA.Due to logistics, I've migrated Secondary first. I now need to bring Primary into HA.I need to ensure that new Primary syncs from Secondary, and not the other way around.Would the best way to ensure thi...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


