
Hey everyone. We have several ASA units, ranging from 5505 to 5555X. Our 5555X is reaching about 55% to 60% CPU during peek hours and we are looking to replace it. Can anyone help me with some tips on what to look at, are HW boxes still the way ...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,338) -
Cisco Bugs
(63) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(282) -
Cisco Secure Firewall Threat Defense (FTD)
(340) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,236) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
I am converting ASA to firepower. The problem is that I need to remove the zones and int ip addresses from the original config as they are being removed and replaced with a new ip schemes. Is there a way to edit the new sfo file to add the new int i...
I've attempted 3 time now to upgrade a 3D7125 from 5.3.0.3 to 5.4.0-763 with it failing at the same stepInstalling Sourcefire 3D Device S3 Upgrade version: 5.4.0-763Local InstallUpdate Installation Failed : [15%] Fatal error: Error running script 200...
Hi Folks, anyone have experience with how to search all the hosts running vulnerable browsers? for eg, if I run the templated report 'Network Risk Report' it has a section "dangerous web browser versions" How do I search within my hosts to pull up ...
Hello Guys , I'm studying Firewall and I performing a NAT Lab to improve my skills. The ideia is be able to access ssh from "Remote_Router" to "Firewall", ISP will perform a static nat from 200.0.0.6 to 172.16.0.2 Outside on "Firewall". I can ping ...
Resolved! Cisco ASA 5506-X problem NAT
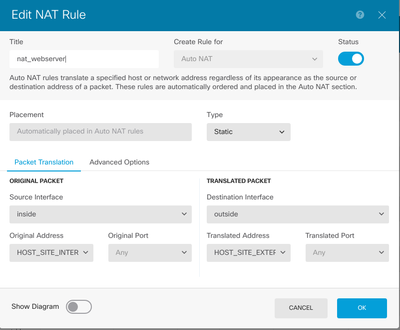
Hello, I need a NAT for the Institution website and created the following rule. Checking the access LOG it gives me the following return and does not arrive at its destination in the IP inside. Does anyone have any ideas ?

I have a Cisco ASA 5512-X and it is discarding any IPv6 packets on the ingress interface. In particular I have an ISP (Comcast) who sends DHCPv6 advertisement and reply XIDs with a hop limit of 0. I reported it to them, but they told me to pound sa...
Hi all, I'm having an issue with Firepower Syslog, for some reason, I get the Syslog from the FMC with (null) in the place where the sender FTD IP or hostname should be. I'm using a pure Firepower installation (not an upgrade from ASA) version 6.3....
Can I deploy firepower (FTD 6.2) between campus core switch and nexus5672UP ? Are there any problem if I deploy like this ?
Hi All, I have a network set up and running for some time where we have an internal network that access the internet via a squid proxy. This high side proxy has two NICs, one connected to the internal network and one connected to the inside interfa...
Please let me know if there is a difference between Singlemode and Multimode in ASA firewall. Also, please let me know the difference between context and mode.
Can FTD Support multiple AD integrations and allow multitenancy support?
I have a Firepower module in my ASA 5506-X and had registered it with my FireSIGHT Management Center. Unfortunately I removed the device from FireSIGHT Management Center and hadn't removed the manager from the Firepower module first. I also reali...
Hi guys I got a situation with an IPsec Tunnel and i don't know what else I need do, this is the situation: I already configured a VPN Tunnel between my Cisco ASA and a Fortigate 100D everything is up (Phase 1 and Phase 2), this tunnel was create...
I bought an asa 5505 but with version 7.4 ... I neede to make it work but so far I can not even ping ..So I can not upgrade to version 9.4 I don't even know if it 's a subnet issue but I keep getting no route found I don't if the problem is a wro...


Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 6 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


