

hi,i setup a simple lab between ISE and CSRv for AAA/RADIUS.i added the device and user in ISE and it works, but not for the enable password on the router.it still uses the 'local' configured enable password. i also couldn't SSH to ASA using the ISE ...
Network Access Control
Cisco Identity Services Engine (ISE), Cisco Access Manager (CAM), Zero Trust Workplace
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Access Control
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
This community is for technical, feature, configuration and deployment questions.
For production deployment issues, please contact the TAC! We will not comment or assist with your TAC case in these forums.
Please see How to Ask the Community for Help for other troubleshooting best practices.
For production deployment issues, please contact the TAC! We will not comment or assist with your TAC case in these forums.
Please see How to Ask the Community for Help for other troubleshooting best practices.
Labels
-
(ISE) Identity Service Engine
(1) -
AAA
(16,836) -
Access Control Server (ACS)
(434) -
Access Manager
(7) -
ACI
(33) -
AMP for Endpoints
(1) -
AnyConnect
(6) -
APIs
(154) -
Appliances
(58) -
Ask the Experts
(1) -
Branch Router
(1) -
Buying Recommendation
(28) -
BYOD
(154) -
Catalyst 2000
(2) -
Catalyst 3000
(1) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 9000
(12) -
Catalyst Switch
(1) -
Catalyst Wireless Controllers
(4) -
Cisco Adaptive Security Appliance (ASA)
(11) -
Cisco Bugs
(52) -
Cisco Cafe
(2) -
Cisco Defense Orchestrator (CDO)
(1) -
Cisco DNA
(1) -
Cisco ENCS
(1) -
Cisco Firepower Device Manager (FDM)
(3) -
Cisco Firepower Management Center (FMC)
(3) -
Cisco Firepower Threat Defense (FTD)
(2) -
Cisco ISE
(1) -
Cisco Secure Firewall
(1) -
Cisco Software
(10) -
Cisco Spaces
(1) -
CISCO START ASEAN
(1) -
Cisco Vulnerability Management
(2) -
Cloud Security
(1) -
Community Bug or Issue
(3) -
Community Feedback Forum
(9) -
Community Ideas
(4) -
Compliance and Posture
(398) -
Data Center Networking
(1) -
Device Admin
(295) -
Endpoint Security
(10) -
Event Analysis
(9) -
Guest
(350) -
Identity Provider
(10) -
Identity Services Engine (ISE)
(14,029) -
Integrated Security
(12) -
Integrations
(284) -
IPS and IDS
(2) -
ISE
(41) -
LAN Switching
(10) -
License
(5) -
Meraki
(4) -
Meraki Switch
(1) -
MFA
(71) -
Multi-Domain
(65) -
NAC
(40) -
Network Access Control
(1) -
Network Management
(76) -
Networking
(1) -
Optical Networking
(1) -
Other Cisco DNA
(2) -
Other Collaboration Applications
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other NAC
(2,820) -
Other Network
(4) -
Other Network Security Topics
(79) -
Other Networking
(5) -
Other Routers
(2) -
Other Routing
(1) -
Other Security Topics
(7) -
Other Switches
(9) -
Other Switching
(6) -
other topics
(1) -
Other VPN Topics
(2) -
Other Wireless Topics
(1) -
Passive Identity
(118) -
Physical Security
(5) -
Policy and Access
(1) -
Profiling
(7) -
RADIUS
(5) -
regional availability
(1) -
Remote Access
(5) -
Routing Protocols
(1) -
Security
(8) -
Security Certifications
(4) -
Security Management
(56) -
Segmentation
(173) -
Support APIs
(1) -
Third Party Integrations
(1) -
Threat Containment
(29) -
vEdge Routers
(1) -
Visibility
(89) -
VPN
(200) -
Vulnerability Management
(2) -
WAN
(1) -
Web Security
(2) -
what's in stock
(1) -
Wi-Fi 6
(1) -
Wired
(459) -
Wireless
(463) -
Wireless LAN Controller
(2) -
Wireless Network Management
(3) -
Wireless Security
(8) -
Wireless Security and Network Management
(2)
- « Previous
- Next »
Forum Posts
Resolved! Windows 10 EAPOL-Logoff
Customer has shared Win 10 machines, with mutiple users. When user A logs off, and user B logs in, it takes close to ~4 minutes for it to get a new IP address and the corresponding SGT. Native supplicant is used and machine connects directly to the s...
Resolved! NAM 4.7 TLS 1.2 ISE 2.6
Team, A customer of mine is doing validation testing for ISE 2.6 and came across FN 70357. https://www.cisco.com/c/en/us/support/docs/field-notices/703/fn70357.html Based on this, it is clear that TLS 1.2 support is not available in ISE 2.6. When w...
Hi guys, We are using ISE2.4 BYOD self registration, we want to differ the qty of device a user can self-registeration, however, there is only a global setting to limit the registered qty, can we do group based setting?
Hi guys!! I've configured an API rest application for applying an ANC policy to an endpoint, but until I excute a CoA ReAuth this policy isn't applied... so I want to apply at the same time ANC policy and CoA from API Rest call... Can anybody help ho...
Resolved! ISE Network Devices Page Disappeared
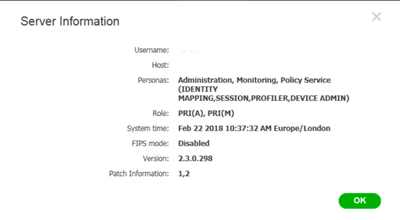
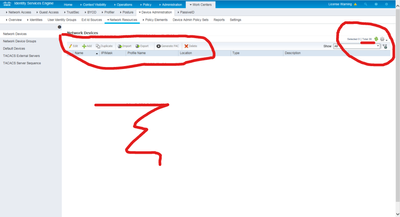
Hello. We have installed two ISE nodes, version 2.3, successfully imported configuration from ACS 5.8, all seemed to work properly. But, after installation of patches 1 and 2, now in Device Administration -> Network Resources -> Network Devices, we c...
I configured a centralized web authentication with users in the Active Directory. The problem is CoA, but it is enable in the ISE and WLC.CoA Problem: WLC : (Cisco Controller) >show radius rfc3576 statisticsRFC-3576 Servers:Server Index.................
I am testing the option of the ISE Certificate Portal. I have created an ISE Certificate Portal to allow users to logon and generate an EAP certificate for their device. When I test with a MacBook and Windows PC the certificate zip downloads and I ca...
Resolved! ISE Sponsor authenticated users timeout
team, in ISE, device authenticated through a sponsor, needs to reauthenticate every 20 min. any idea how to change this and make it at least 8h? i already checked the WLC and the timeout value is set to maximum 65535. anything else to modify?
Resolved! Renew certificate of a deleted node
Hello, I have an ISE with two PAN and two PSN. The certificate for admin usage is expired. I have deleted the secondary node and now when I try to register it back, I get the expired certificate error. I will renew the certificate. My concern is how...
Resolved! Cisco ISE VPN POSTURE notworking
Hi All , i have cisco ISE SSH VPN , posture scan i snot working . on Anyconnect Posture module showing '' No Policy Server Detected '' from the End-point -CMD , nslookup to the ISE server FQDN is showing timeout (Screenshot is attached )
Hello, This is my first post here, I was searching on cisco communities and I find the following script to redirect the login page to create and account<script> $(document).on('pageshow', function() { if (!(/selfregistrationcancel|selfregistrationsuc...
Hi Team, Please support to transfer the license for our ISE VM maj of version 1.4 to 2.4. Old license: GHBMEA88UHI Thank you in advance.Kind Regards,Samson
Resolved! ISE deployment with 9 PSNs
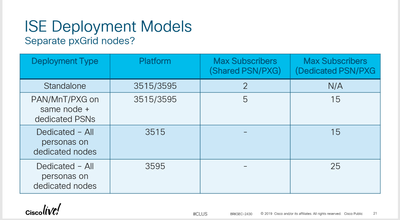
hi All, I need someone to confirm one thing about deployment for 9 PSNs. I remember from most of the presentations that whenever you have more than 5 PSN you need to split PAN from MnT so how to interpret the following pictures? different presentati...

Hello, Do we have any options in cisco ISE to identify, which certificates has been used by endpoint to get authenticated.Is there anyways in pulling report based on above mentioned statement. CISCO ISE 2.4 patch 10 Thanks and regards Afeez Mali
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 04-27-2026 04:44 PM | ||
| 04-22-2026 01:25 PM | ||
| 03-05-2026 07:50 AM | ||
| 02-18-2026 03:44 PM | ||
| 02-10-2026 08:46 AM |


New solutions


