
Hi All, I'll be installing a new (single) Cisco ASA soon, and i need to connect that directly to a Active/Standby Cluster. How should i configure this on the new ASA Side? Should i create a "Redundant Interface" and connect the Active firewall to t...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,339) -
Cisco Bugs
(65) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(288) -
Cisco Secure Firewall Threat Defense (FTD)
(343) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(39) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,663) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(3) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Hi everyone, I am wondering if there is a possibility to allow inter-interface traffic with acls without allowing all traffic on the same security level. So first disallow everything and then allow traffic with normal acls. Is it not possible by de...
Hi,I am getting crazy trying to understand and configure outside access to our customer router with Zone-Based Firewall.Until now the customer was running IOS classic firewall and I decide to configure Zone-based firewall as it will give more flexibi...
I am trying to push a Sensitive Data Detection Policy to detect email and possible passwords being entered in a URL, but whenever I deploy the policy I am given a Snort validation error. FMC 6.2.3.2 ASA with FP Module 6.2.2 Here is the RegEx - Noth...
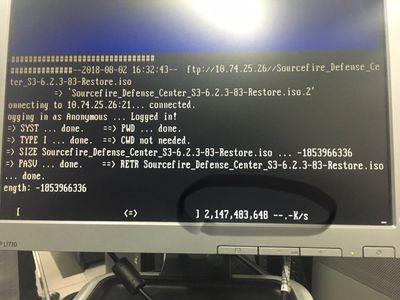
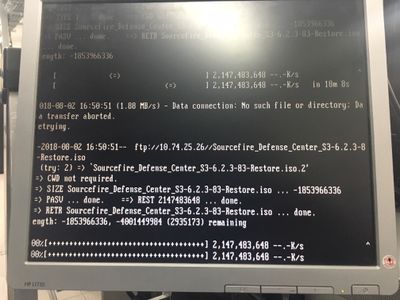
Hello everyone Today I have a weird error during the iso transfer with a Defense Center 750. I'm making the reimage process for that firesight appliance because it had the 5.4.0 software, I start the download and mount ISO step, but the file transf...
Hello, How do I submit for a website to be unblocked or de-listed from the Cisco website malware database? This website was hacked last year, has been rebuilt from the group up, and yet Cisco thinks it's malicious. We've triple checked all logs, co...
I've created a test rule to block .study, .accountant, .party, .click, .top, .life, .yokohama, .ml TLD's I first created a URL objects and then put them in the group TLD_Top10_abused Created a test policy under users with only me with block with rese...
We have recently upgraded our firepower 8350 to 6.2.3.4 and we have started seeing high CPU instance for SNORT processes and in one of the case we hit major slowness and high traffic drop rates. We have engaged TAC - almost 3 times now and each en...
Does anyone know if it is possible to remotely turn on the power on a FMC 4000 appliance via the ILO connection? I have an open TAC case where we need to do a BIOS upgrade due to a firmware bug. According to TAC, after the firmware is installed the a...
Does anyone know a way to easily, statically NAT one /24 address to another /24 address, while keeping the host addresses the same. I was thinking something like this, but it doesn't seem to work. I'm trying to avoid configuring a static NAT transl...
Greetings All, Does Cisco have some form of software simulation that I can use for training on the ASA firewall series? Where can I download or purchase? Thanks in advance
Hi guys, I come today with some funny/tricky ACL issue. I have this classic setup: - ASA (default route to the router) <----> 4000 series ISR router - ISR router has two interfaces Gi0/0 toward ASA and Gi0/1 toward ISP - default route is install...
Hello guys, A customer bought a CISCO ASA5508-X Threat Defense and it was delivered with Firepower image but we are not going to use all of the firepower services. How can i disable all the firepower services and related stuffs here ? I just want o...
I am doing a migration from checkpoint R77 to FTD. On checkpoint inbound rules have defined public address in ACL destination which then natted to static internal addresses. In FTD when I have done the conversion it still holding those pub ip's in ...
Just starting to configure our ASA 5525X HA pair to support AnyConnect clients. We currently have several IKEv1 VPNs terminating on our outside interface so I am concerned about the impact of enabling webvpn on the outside as well... is there any ser...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 11-06-2026 12:20 AM | ||
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


