
Hello,Friend I am really confused in configuring a site to site vpn;can somebody help me by giving me the way forward for sorting out the issue?I am configuring a site to site vpn where the remote IP (public) is used twice on my firewall as it has to...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(10) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,335) -
Cisco Bugs
(60) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(139) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(55) -
Cisco Secure Firewall Management Center (FMC)
(275) -
Cisco Secure Firewall Threat Defense (FTD)
(329) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(21) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(27) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(88) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,234) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Open Source and Open Standards
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Automation Analytics Topics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other IP Telephony
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,660) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(28) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Hello, M name is Bernard and I would like to request some assistance with an ASA 5505 which is giving me the error "unable to launch device manager from xxx.xxx.xxx.xxx(x represents the IP address of the ASA) when I launch the ASDM application.I'm n...
Hi All, I am doing a new deployment of Virtual Firepower Thread Defense (FTDv) using ESXI and using ACI as bridge domain for my infrastructure. My problem is the FTDv is running in Transparent mode between 2 routers and these routers will be runn...
Dear all,Please let me know bellow.I want to allow only google mail using source and destination concept.How to configure source and destination using i.p and port number if we are using dynamic i.p Thank you Regardssuresh
Hi, I have a new ASA5508 where i installed the new FTD 6.2 I think the interface looks OK, but i cant find out how to monitor the site2site VPN Can anyone tell me o i can see status of the VPN tunnels, and how to see some log if i have a tunnel with ...
I am wanting to deploy a FTD virtual into Azure using the pre-built on the from Azure Marketplace. I want it to be in Routed Mode and to have an Inside, Outside, a DMZ interface, and finally an interface for Management.It sounds like the FTDv only s...
Hi I am planning to install ASA 9.9 code on FTD 4150, do we need different management IP addresses to FTD and ASA or do they share same management IP address? I believe FTD 2100 Model shares same management IP address between FTD and ASA if we inst...
My ASA reboots without notice once a day and my syslog shows no signs on what causing it. What should I be looking for or set the logging where I can catch it.Thanks
Hi, I just want to make sure i have the correct upgrade path in mind. All are using ASA with NGIPS. Current FP build is 6.1.0.5 I have upgraded our FMC to 6.2.2.2-109 For the modules i would import the following updates into FMC to successfully...
Hello all, Seen cases where nat is done on the border gateway router. Just wondering is there any advantage of creating nat on the firewall as against the BGR?
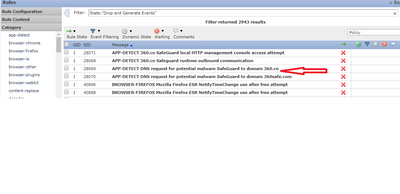
We are facing issue with intrusion policy that is not working as per the configuration. We have a intrusion policy in which multiple signature state are"Drop and Generate Events" and our base policy is "Balanced security and Connectivity". The the in...


Hi Guys, we are going to add 1000 Network object to ASA5516 with Firepower on 6.2.I would like to know is this possible? or are there any information about network objects limitation? much appreciate. rgds,Cuong.
I can ping the host that is on the other side of the ipsec tunnel but i cannot monitor it via SLA. PCVST-ASA# ping inside 172.31.56.152Type escape sequence to abort.Sending 5, 100-byte ICMP Echos to 172.31.56.152, timeout is 2 seconds:!!!!!Success ...
I have a IPsec tunnet to amazon VPC client. The tunnel is up and the VPC side can get access to my resources but I cannot get access to VPC side. The client claims that inbound security rules are setup to allow my subnet. How can I troubleshoot if my...
i deployed FMC version 6.2.2 which managing FTD appliance , i am trying to generate report for specific rule with its connection events for last 3 days in excel format but after generating report it give me on the last two hours , i tried to exceed ...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-24-2026 02:14 AM | ||
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |


