
Hi GuysLAN (inside) network - 192.168.10.0/24WAN (outside)network - for eg 137.14.191.12/28Device: Cisco Firepower 2100 series managed by vFMC I have around 15 servers residing inside the campus that needs to be opened for public. Each server has dif...
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,338) -
Cisco Bugs
(65) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(140) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(57) -
Cisco Secure Firewall Management Center (FMC)
(282) -
Cisco Secure Firewall Threat Defense (FTD)
(341) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(39) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(3) -
Other Network Security Topics
(10,662) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(5) -
Security Management
(566) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Hi, We have two Firepower 4110 units that only have 2 logical interfaces. One is from a Gigamon tap and configured as a passive interfaces and the other is the management interface. We are using these units essentially as out of band IDS units. They ...
Dear All, Please, I need guidelines on how to configure inspection policy for access rule on ASA Firepower for inbound traffic.Currently, I have 3 policies configured as following1. default policy2. Policy for outbound traffics inspection which worki...
Resolved! FirePower 8000 Device FQDN feature
I have Firepower 8000 Devices at Core Layer of my network. Code version for these Devices are 6.3.0.1. FMC for this device managed from is 6.4.0.4. Does Firepower 8000 support FQDN Objects ? if yes can you provide reference to it ? and tested it ?
Hi guys, I'm running a firepoower 2100 with asa image 9.12.2. An interface of the firewall is connected to production network in a uncontrolled space. For this reason I was trying to check some sort of network attack on that interface to double check...
Hello Cisco Community I have configured the above firewall using Firepower Device Manager , i am a bit new to this GUI interface, and i am having issues with the access control. I have set up all my objects with their appropriate IP addresses and hav...
My understanding is the syslog is based on the "Real-Time Log view which has the columns "Severity", "Date - Month, Year(Year to be remove)", "Time", "Syslog ID", "Source IP", "Destination IP", "Destination Port" and " Description" How can I remove f...
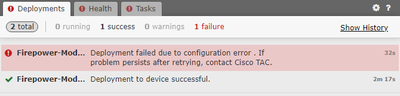
Dear Community i'm facing the following error when i deploy the Access Control policyone of the 5525x firepower succeed while the other fail.the FMC is a virtual appliance.even when i deploy a basic any to any policy
we have an ASA 5500x environment like this.Main site 5516xremote sites 5508 and 5506x we are using a Firepower Service VM to manage all the firepower services on the devices.we are not in FTD mode. since the 5506x w/firepower is now EOL, is it possib...
Resolved! SI URL whitelisting not working
Hi, I have enabled DPI inspection on my FTD units. When I whitelist a URL by domain or URL, via the connection events in the fmc, I am still getting blocked for the URL category. Per the event log, it is getting de-crypt and the behavior is same with...
Dears,Happy new year to all; I have an issue regarding retrieving web content for web service from my webvpn (clientless-ssl ), please advise me regarding this issue as attached. ASA Model: 5515Version: 9.12 Thanks.
I am trying to send a POST request to the Firepower REST API. See the following information:POST accesspoliciesRequest Type: POSTDescription: Creates an access control policy with the specified parameters.URL: /api/fmc_config/v1/domain/{domain_UUID}/...
can anyone tell me the summarized steps on how to self generate a CA and self sign a certificate to use in ssl decryption rules?
Hello Cisco community! My name is Steven Blake and I’m retired military currently working as a contractor for an Air National Guard Unit in Reno Nevada. We have some pretty old Cisco equipment that we are looking to dispose of. This equipment has ...
Being these modules were unable to license signatures for a couple of years now, is there any use for the AIP-SSM-10 aside from a glorified paperweight? I did some cursory web searches, and I didn't find anything that would indicate a method to re-pu...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 4 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


