Need to setup control plane blocks for two OUTSIDE interfaces.Only have production ASA's running 9.1.x so can't "try it out".Will the below work, or is there an easier method?BLCKCOUNTRY is an object group (not shown) with 200 subnets to block.10.11....
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(10) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,336) -
Cisco Bugs
(61) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(139) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(55) -
Cisco Secure Firewall Management Center (FMC)
(280) -
Cisco Secure Firewall Threat Defense (FTD)
(334) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(21) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(27) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(88) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Open Source and Open Standards
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Automation Analytics Topics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other IP Telephony
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,661) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(28) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
I have configured a rule in the Default NAC that is supposed to block a Layer 7 protocol application. When I analyze hit counts, it shows the rule has been matched. And when I analyze connection events, the traffic is showing as dropped. This is the ...
Dear members, I just logged on to the firepower management center and noticed that its failing deployment for the below firewall and after taking deeper look I noticed the SFR is stuck in Init mode. I tried to reset, shutdown and reload with no succe...
Resolved! Firepower - Max ACL Limits
Hello, What are the ACL limits on the Firepower family running ASA code? I've found documentation regarding the ASA hardware family but nothing related to the new Firepower appliances. I suppose the limitations would be much higher because of the a...
Hi,IF we do not remove packet capture on ASA does it cause CPU to spike?Regards,Krishna
I have firewall FPR 3110 with ASA 9.17, but when I try to do a commit buffer in FXOS mode, a error apear: Error: commit disabled while in appliance mode cisco asa. How can I solve this problem to enable the OIDs to monitor chassis characteristics and...
Hey Guys,I have got a problem with a VTI site to site tunnel we created between two ASA's.The VTI tunnel is up and running and we can use it to access the other site, however on site B we have an extra VLAN which also need access to the subnet on the...
Hi All,in which format we can send logs to any syslog server from FMC4700 version 7.1?Also what are the different type of logs can be Sent to syslog from FMC?
Hello.CyberOps VM in networking academy is not booting from Virtualbox. It will continue to stop in the following states:Please help me.

Hi All, I need to downgrade my lab FTD from 7.2.5 to 7.2.3- (I dont suppose i have revert option as its been more than 30 days). I understand i need to re-image but i have the below options in my firewall. What happens if i do the below? is it the sa...
Hi All, I have tried all forms of sw-module module uninstallresetreloadrecover stoprecover boot (setting the boot image to my .img file in disk0Can anyone help or should I raise a tac case??
HiI have an FMC managed 1140 device on FTD 7.2.4, as of this morning I was able to SSH to it on the management interface, now I am not able to SSH, I also added a policy to try to SSH via the other interfaces but without luck, this is what I get:kex_...
I have some external systems which are sending data to a syslog server on UDP port 514 which is behind an FTDv(v6.6.7.1) which is managed by a Cisco FMC (v6.6.7.1), I have a rule in the ACP on the FTD to allow traffic from these external systems on p...
Hey all I setup smart card 2FA with firepower previously. The way it worked is in order to establish VPN the smartcard was looked at by the anyconnect client for certificate for which a PIN was entered then VPN established. I am trying to do the same...
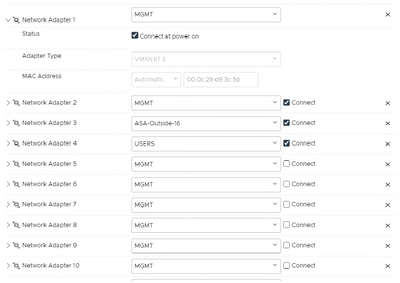
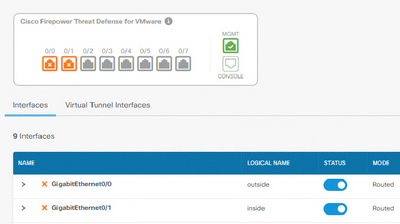
Hello!I instlled FTDv (7.3.1-19) on ESXI 8.All interfaces down, instead Managemet. On ESXI it configured as VMXNET3.On ESXI side its attach and connected, but on FTDv side its in DOWN status!ESXiFTDv > show interface ip brief Interface IP-Address OK...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 10-05-2026 02:05 PM | ||
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 4 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |