
Resolved! Migration to Data Store
Hi,Is it possible to migrate an existing SNA deployment where all the components are virtual to the Data Store architecture?Regards
Hi,Is it possible to migrate an existing SNA deployment where all the components are virtual to the Data Store architecture?Regards
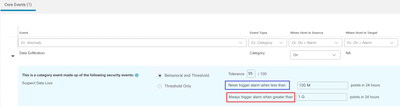
I am reading the Cisco Stealthwatch Desktop Client User Guide and the following section about the Variance-based alarms Never trigger alarm when less than: Also known as the minimumthreshold, this is a static value that indicates the lowest value to ...
What does it mean? - flow collector longest export exceeded I have some allarms like that for my devices, maybe I need to increase intervals for monitor or exporter?
helloeverybody i hope your doing well i have asked this question many time i need your help in our network infrastructure we have cisco catalyst switch 9200 version 17.6we have Qualys scan for vulnerability there is a certain vulnerability that would...
Dear, I would like to ask if it is possible to make automatic reports in SNA. Currently we generate reports manually, but our client wants to automate them.There is the mentioned process, can you share information with me, I remain attentive thanks.
after upgrade to 7.5.0 I can't upload pathes We couldn’t complete the upload. Check the file and try again, or please contact Cisco Support. It's the bug - https://bst.cloudapps.cisco.com/bugsearch/bug/CSCwi37950 and Workaround: After gaining access ...
Can someone help me with understanding what each of these Advanced options means and in which use cases I should check or uncheck these?
The scenario is that all traffic ingesting to flow sensor is north-south, and all hosts are NATed by public IPs. Currently, there is no east-west traffic. However, if east-west traffic were to ingest, would the hosts be visible as endpoints or networ...
Anybody know if the c9606R and c9300X-24Y can work with Stealthwatch? I try to configure on the c9606R and c9300x-24y flow record REC-IN match ipv4 source address match ipv4 destination address match transport source-port match transport destinatio...
I am unable to manually assign ANC policies to hosts in the Secure Network Analytics Host Report section. When I inspect a specific host and try to assign one at the Host Summary Pane, I am receiving this error: We encountered an error from one or mo...
Error " The authentication service was unable to fulfill your request. If this problem persists, contact your administrator."
What is the best method for getting security events and analytics into an external SIEM (Splunk)? Thank youPhilip
We wanted to integrate our IBM SOAR with Cisco Threat Grid and it requested for an API key. From where we can get the key and also does we need license to integrate with Cisco Threat Grid?
Hi, I need an advice. I want to be allarmed when one host eirher consume bandwith above 30 Mbps, I made new policy in the "Core events" - single host policy but it seems doesn't work What am I doing wrong?

is there a way to reset all of the counters/data through the GUI in Stealthwatch? i have a different setup and want to see data only AFTER the new settings so that i can tell if it is actually working like it is supposed to.
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
| Subject | Author | Posted |
|---|---|---|
| 09-30-2026 09:32 PM | ||
| 08-12-2026 08:15 AM | ||
| 07-09-2026 04:56 PM | ||
| 06-04-2026 11:28 PM | ||
| 03-08-2026 11:12 PM |

