
Hi All,I am facing an issue which I am not able to trace the destination ip and port of the whatsapp application in order to open it on the firewall?any advise ?Thanks
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,335) -
Cisco Bugs
(60) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(138) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(54) -
Cisco Secure Firewall Management Center (FMC)
(273) -
Cisco Secure Firewall Threat Defense (FTD)
(325) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(237) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,234) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,660) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Resolved! Old NAT ASA Config Question
Hello Network Gurus,Just trying to figure out what is this NAT config for?global (outside) 1 interfacenat (inside) 1 0.0.0.0 0.0.0.0static (inside,outside) 10.17.1.5 10.17.1.5 netmask 255.255.255.255Saw this access list command as well:access-group O...
I'm trying to set up a transparent mode FTD on the FMC to allow L2 multicast IEC61850 goose packets with a VLAN tag to pass between inside and outside sub-interfaces.1. I created a BVI to bind inside and outside sub-interfaces but have no IP address....
we have three pairs of FTD 4100 series managed by an FMC 1600, yesterday we got an error on one of the FTD that says: Policy "policy name" has been altered since "timestamp". Retry deployment we didn't deployed anything on this particular device. De...

Resolved! FMCv300 Resources
Hello community,currently we have started with implementation of FMCv in our network.Since we need to manage more than 25 senors I suppose there is no other option than to go to FMCv300.My question is, is it possible to modify/ downsize resources req...
Hi All,I have a cisco FPR 2130 i have connected eth1/13 and eth1/14 with 10G LR SFPs with a device called IXIA its a point to point connectivity. On IXIA i have an SFP called (Ixia, QSFP+ 40GBASE-PLR4 40GE pluggable optical transceiver, SMF (singlemo...
Hello. I've been working with the Cisco API interacting with different FMCs for a while, and I notice that every physical device has the same domain UUID, which is "e276abec-e0f2-11e3-8169-6d9ed49b625f".In my side of the API programming I considered ...
I'm having issues with my networks not being able to resolve websites. I'm trying to configure DNS servers on internal segments without putting them on the public network. So basically, port forwarding ideally, I would like to have one DNS server in ...
Dears, I have three questions, Please answer Please find the attached error. whenever i navigate to edit the ACP , i get a pop-up as per the attached , also when i save after doing any changes i get an a attached pop-up error, hence it is a bug ...
Resolved! Cannot ping across Cisco Firewall 2110
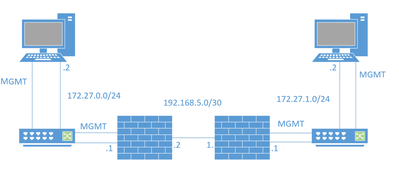
I have a bit of a unique situation which I am struggling with. The topology is a bit weird so let me explain the end goal. We want to physically separate the two sides of this network into two autonomous networks with each side having their own firew...
Hello,I have a site to site vpn that works just fine, however when I tried to NAT traffic from my INTERNAL network with a pool NATPOOL over that vpn tunnel, the traffic simply doesn't work, what I tried is to implement the following nat rule but stil...
Resolved! Edit CSM_FW_ACL_ on Cisco FTD2100?
I can't find anywhere on the FMC on how to update this. Can't find any documentation either.
Is there a way to limit the amount of SSH sessions to the FTD CLI?
Hi,The result I am trying to achieve is blocking the ICMP traffic from 192.168.100.101 pc (inside traffic) to 192.168.101.00/24 (outside) trafic.I've configured an ACL, but for some reason the ICMP still travel through ASA:access-list outside line 1 ...
I noticed one of the policies on the FMC is out of date i.e not updated/deployed on the Firewall.I am not aware what changes were done on the policy and I want to avoid going through each and every rule to find that out.Is there way I can rollback ch...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM | ||
| 08-10-2026 08:58 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |


