
Hello I have an ASA 5525-X versio 9.8 and i am trying to install firepower module 6.2.2 but i am still having this error.Module sfr did not respond to session request.Here you are the show version and another command.
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(10) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,336) -
Cisco Bugs
(61) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(139) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(55) -
Cisco Secure Firewall Management Center (FMC)
(278) -
Cisco Secure Firewall Threat Defense (FTD)
(332) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(21) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(27) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(88) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,235) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Open Source and Open Standards
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Automation Analytics Topics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other IP Telephony
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,661) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(28) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
HiI have few ASA's in my network for which when I try to do session SFRIam getting the message :"Opening command session with module sfr.Module sfr did not respond to session request." What could be the reasons for getting the above messages ?Has the...
Hi,I'm trying to configure my first Firepower 1010 replacing Fortigate. Few things I'm stuck at the moment.1. How can I configure dhcp options like 150? I don't see that options anywhere in the FDM gui. 2. Is there anything like software switch fe...
Hello, I need to configure an ASA 5545 as a pass-through filter for devices (two, with one inside, and two outside interfaces each) that are connected directly to the internet. They do not want to use Firepower. I have configured one-to one NATs f...
Good morning I am trying to figure out how to configure vlan ACL to filter mac addresses. And cannot make it work! The goal is to block all mac-addresses inside vlan except those are permitted. I found a great article which declares the same in the o...
Resolved! FMC/FTD question
Hello Does anyone know if Firepower would block packets with a via header added to them.?? Thanks
I have a setup with 4 HA pairs of FTD's in the FMC Global domain all running 6.6.4.x. We intend to deploy many more, so have decided we need to segregate access based on geo-location of the FTD's. So I need to create new subdomains for the new FTD's ...
Currently i am required to enable 2 PPPoE ISP link on the ASA, this specific PPPoE link requires to be tag to vlan 500 for it to be working.Since i am unable to created same VLAN ID on separate subinteface on the ASA.Any way i can configure both ISP ...
We are switching over a section of our environment from McAfee Network Security to Firepower. We have several different policies for different customers. McAfee uses a combination of NSP rules, CVEs, and other ways to identify and categorize intrusti...
Where can you find the TSAgent-1.3.0.exe for Cisco Firepower agent? Can't seem to find in downloads anywhere.
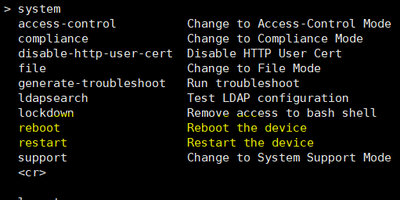
What are different between reboot and restart on SFR module?
In the sho route command below you'll see that the ASA sees three paths to the network 10.1.48.0/23. But it has selected 10.1.0.8 as the preferred path. How does the ASA end up selecting it as the preferred next hop?ASA01/pri/act# sho route 10.1.48.0...
Resolved! Site-to-Site VPN password best practices
Hello, we have 15+ home users with Cisco C881k9 routers that are doing an automatic ikev2 site-to-site VPN connection back to our head-end VPN concentrating Cisco ASA 5525-X firewall. The home users obviously have DHCP public IP addresses. Does anyon...
Hi I have an ASA 5525-X.There is no configuration on the ASA but after executing these commands debug sfr errordebug sfr eventsdebug sfr messagesdebug cplanedebug module-booti have this error below.cp_check_connection: handle -1, conflicts with conne...
Hi, I am trying to integrate Cisco CSM to ISE so that I can resolve the security group tags from CSM. I understand that in order to to be able to retrieve the group tags with a search name/tag in "Security group selector" we need to configure ISE ...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 2 | |
| 1 | |
| 1 |


