
My 3rd party cert expired on my ISE and I got another. I am just having a terrible time figuring out how to get it in and if I even have the correct type of cert
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,335) -
Cisco Bugs
(60) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(138) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(54) -
Cisco Secure Firewall Management Center (FMC)
(273) -
Cisco Secure Firewall Threat Defense (FTD)
(325) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(237) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,234) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,660) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
Resolved! FMC/FTD NAT
HiDoes anyone have any suggestions on why I am getting NAT failures on FTD I have configured a rule allowing WLC inside to outside on ports 16666/16667 and ETHIP(97) the WLC is part of a NAT rule Natting all rfc1918 to an address.??? Thanks
Hello, I've noticed that I cant create vlan interfaces on this model but I use to be able to on older model like the ASA5505. Has this been changed ? I'm new to the X series. what's the equivalent of doing this on the 5555-X ?
Hi, I'm currently running FMC version 6.6.1 and I have two FTDs running 6.6.0.1 and want to make sure I choose the correct next step to upgrade the FTDs. When I go to download updates the only one I see for the FTDs is Cisco FTD SSP FP2K Patch 6.6.0....
I want to redundant the interface of the ASA.The equipment is a Firepower 1140.There is no interface redudant command.Is there a good way??

Hello,I am facing an issue with SSH/HTTPS management access on a Firepower 4100. After un-boxing the device, I consoled in and ran through the initial setup. I assigned the IP, subnet, hostname, default gateway, and IP blocks on the interface. I a...


Hello for everybody. Not so far away we updated our FMC and FTD from 6.4.0 to 6.6.1 software version. Today, when trying to add auto nat rule for the test network, I faced the following problem. Auto nat rules can not be configured on more than one s...
Hi All , i have installed FTD 6.2 on Cisco ASA 5508X , and by mistake i have selected FDM during installation . is there any way to convert it to FMC. Please advice
We are trying to have Duo Proxy use ISE to authenticate and not be a proxy to AD or another Radius Server. Has anyone gotten this to work before? Solution: Anyconnect VPN with DUO MFA
I have an active/passive ASA cluster. From the shell of the master unit, is it possible to SSH over to the standby unit?
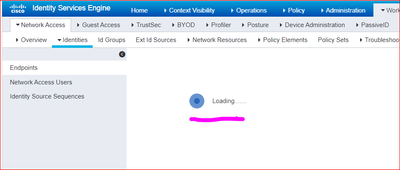
Resolved! One page in ISE is keeping loading
ISE2.7 can work well. but suddenly only one page cannot be showing up and keeping "loading" status. Please see below page.Thank you
Hi! I have a question regarding DDNS and FTD. We get a DHCP address from our ISP on our outside interface which we're using for our VPN clients. We want to bind this address to a more convient name for example: vpn.example.com. I've read about DynD...
Dear community,we have recently noticed several false positives on our IPS based on Firepower Managment Center, in particular signatures: MALWARE-OTHER Win.Trojan.FANCYBEAR variant binary download attempt (1:56933:1)MALWARE-OTHER Win.Malware.Ursu-982...
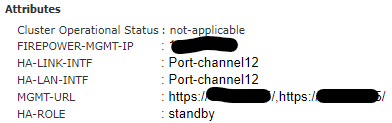
Hi team,The FMC is generating the alert like below.SECONDARY (xxxxxxxx) FAILOVER_STATE_STANDBY_FAILED (Check peer event for reason)Both FTD 9300 are in HA over a port-channel. I have checked both port-channel physical interfaces are in matching the ...

Hello Communityi am tryig to do PBR flex config in my lab environment . 1. I have 2 internal subnets 10.1.1.0 /24 and 192.168.1.0/24 2. i want 10.1 should take isp-1 and 192.168 should take ISP-23. did extended ACL and tried Flex config , but getting...
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM | ||
| 08-10-2026 08:58 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |


