
After upgrading to 6.2.2.2-109 I received a warning that the application rule doesn't match any applications. The rule was set to match evasive/stealth tactics. When I check the rule, there's no tags or categories available. Was this removed ...
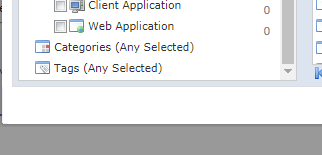
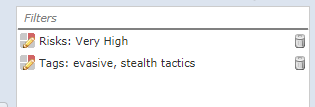
After upgrading to 6.2.2.2-109 I received a warning that the application rule doesn't match any applications. The rule was set to match evasive/stealth tactics. When I check the rule, there's no tags or categories available. Was this removed ...
I want to make sure I'm not missing an alternative to managing FTD with FMC over IPSec.Currently my FTD installations at remote locations are anxiety-ridden. I'm fortunate in that I've been able to lab the FTD locally and deploy a config from our FMC...
ASA5506 ver. 5.4.1 When I try to upload an update file (Network Sensor Parch 5.4.1.8) from my computer in ASDM console, I get an error Bad Gateway "The proxy server received an invalid respose from an upstream server”.
Hello, I an in the process of installing a FP2110 with an ASA image. The version installed is 9.9.2. I cannot connect via SSH. ASDM runs without a problem. This is the output of 'ssh debug 128': server version string:SSH-2.0-Cisco-1.25SSH0: recei...
Hello tech, I am updating all the sfr from 6.0 to 6.1. But one of the sfr is not succeed from 5.4.1 to 6.0. So I image the sfr with the new image 6.0.0.5. The image shows everything okay. But after upload the 6.0.0.5 pkg, the sfr is sitll in recovery...
Dear ALL, Good Morning, i am quite new in Cisco ASA, i have 2 same security interface level 100 in the Cisco Asa, interface 0/1 and interface 0/2, i have to Map Network Drive for Server from one interface to another, i did successfully make both si...
Cisco ASA with FirePOWER Services include Cisco ASA firewalling, AVC, URL filtering, NGIPS, and AMP. Please I need information about AVC, like what are the applicacion web 2.0 and widgets that do control.
Hi Team , Is it possible to pass clear text traffic for same source and destination if one IPSEC tunnel is already configured for same source and destination.
Not sure it it's even possible, have never used ASA. We have been tasked with implementing multifactor authentication. Our plan is to use an ASA vpn with RSA. But our current VPN access is with TMG servers that are configured with their own access p...
I'm trying to block the ESMTP EHLO AUTH response message on an ASA version 9.4(4)16 from coming to the client from the server. The application does not support disabling authentication if the server indicates it is supported, but the server is not ma...
I have locked down management access to our FMCs and new sensors (4100s) for select IP subnets & ports, I am looking at doing the same thing for our legacy sensors (7120/8250). I can't seem to locate where you would specify an access control list f...
I am new to Cisco and was thrown into this. When looking at the Traffic Status is this measuring the speed or the amount of data being transferred? Outside Interface Traffic Usage Input kbps :59599 Output kbps: 30612
HI All, is it possible to connect lets say a host or server directly to one of the 1GB copper or SFP interfaces and use that port as an access port? I know typically the firewall ports are routed ports but, you can also make these ports trunking/su...
Hi, I have multiple customer firewall context running on ASA. As part of the firewall review and strengthening the Security, wanted to monitor and findout the UNUSED FIREWALL RULES and NAT ENTRIES, so that the same can be deleted after confirming tha...
I have been told to block all IPs outside of the United States to a particular server on the inside interface. My plan is to make an allow ACL for an object-group that contains the network0objects for ALL of the subnets currently registered to the U...
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
| Subject | Author | Posted |
|---|---|---|
| 11-14-2026 01:46 AM | ||
| 11-12-2026 11:33 AM | ||
| 11-12-2026 12:41 AM | ||
| 11-06-2026 12:20 AM | ||
| 09-22-2026 04:13 PM |
| User | Count |
|---|---|
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |



