
I am looking into deploying a ASAv in AWS but it has to be FIPS 140-2 certified. I have searched all over the net and found nothing showing the ASAv is or is not FIPS compliant. Does anyone know where this documentation can be
Network Security
Engage with peers and experts on network security topics such as Secure Firewall Threat Defense, Adaptive Security Appliance, Secure Firewall Management Center, and Security Cloud Control.
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Showing results for
- Cisco Community
- Technology and Support
- Security
- Network Security
Options
- Mark all as New
- Mark all as Read
- Float this item to the top
- Subscribe
- Bookmark
- Subscribe to RSS Feed
- Threaded format
- Linear Format
- Sort by Topic Start Date
Labels
-
AAA
(9) -
Access Control Server (ACS)
(6) -
Access List
(4) -
ACI
(10) -
Advanced Threats
(1) -
AMP for Endpoints
(1) -
AnyConnect
(2) -
APIs
(1) -
Appliances
(17) -
ASA
(1) -
Branch Router
(1) -
Buying Recommendation
(81) -
Catalyst 2000
(1) -
Catalyst 3000
(2) -
Catalyst 4000
(1) -
Catalyst 6000
(1) -
Catalyst 8000
(1) -
Catalyst 9000
(2) -
Catalyst Switch
(3) -
Catalyst Wireless Controllers
(1) -
Cisco
(1) -
Cisco Adaptive Security Appliance (ASA)
(9,335) -
Cisco Bugs
(60) -
Cisco Cafe
(15) -
Cisco CLI Analyzer
(1) -
Cisco Cloud Services Router
(1) -
Cisco Defense Orchestrator (CDO)
(138) -
Cisco Firepower Device Manager (FDM)
(768) -
Cisco Firepower Management Center (FMC)
(2,700) -
Cisco Firepower Threat Defense (FTD)
(2,986) -
Cisco Press Cafe
(1) -
Cisco Secure Firewall Device Management (FDM)
(55) -
Cisco Secure Firewall Management Center (FMC)
(275) -
Cisco Secure Firewall Threat Defense (FTD)
(328) -
Cisco Security Cloud Control
(17) -
Cisco Security Manager (CSM)
(3) -
Cisco Software
(20) -
CISCO START ANZ
(1) -
Cisco Threat Response
(1) -
Cisco Vulnerability Management
(45) -
Cloud
(1) -
Cloud Provisioning
(1) -
Cloud Security
(2) -
Community Bug or Issue
(1) -
Community Feedback Forum
(26) -
Community Ideas
(12) -
Compliance and Posture
(1) -
Crypto
(1) -
CSC Content with No Valid Community to Post
(1) -
CUBE
(1) -
CUCM
(1) -
Data Center Networking
(1) -
Device Admin
(15) -
EEM Scripting
(1) -
Emergency Responder
(1) -
Endpoint Security
(6) -
Enterprise Agreement
(1) -
Event Analysis
(238) -
FirePOWER
(1) -
Firepower Chassis Manager (FCM)
(2) -
Firepower Device Manager (FDM)
(14) -
Firepower Management Center (FMC)
(383) -
Firepower Threat Defense (FTD)
(206) -
Firewall Migration Manager (FMM)
(1) -
Firewall Migration Tool (FMT)
(38) -
Firewalls
(1,051) -
FMC
(1) -
General
(2) -
Guest
(1) -
Identity Services Engine (ISE)
(8) -
IE3300
(1) -
Integrated Security
(8) -
Integrated Security Architecture
(1) -
Integrations
(4) -
Investigation
(2) -
iOS
(1) -
IPS and IDS
(6,519) -
IPS and IDS1
(1) -
IPS-IDS
(1) -
IPSEC
(1) -
IPv6 Configuration
(1) -
ISE
(1) -
LAN Switching
(6) -
License
(307) -
MPLS
(1) -
Multicloud Defense
(2) -
Network Management
(87) -
Network Security
(2) -
NFVIS
(1) -
NGFW Firewalls
(37,234) -
NGIPS
(1,794) -
Online Tools and Resources
(1) -
Optical Networking
(3) -
Optics
(1) -
Other Collaboration Topics
(1) -
Other Community Feedback
(3) -
Other Firewalls
(1) -
Other NAC
(18) -
Other Network
(2) -
Other Network Security Topics
(10,660) -
Other Networking
(9) -
Other Routers
(8) -
Other Routing
(22) -
Other Routing and Switching topics
(2) -
Other Security
(1) -
Other Security Topics
(18) -
Other Switches
(12) -
Other Switching
(4) -
Physical Security
(19) -
Policy and Access
(2) -
Prioritization
(3) -
Remote Access
(1) -
Room Endpoints
(1) -
Routing Protocols
(8) -
SD-WAN Security
(1) -
Security
(4) -
Security Management
(565) -
Segmentation
(3) -
Service Providers
(1) -
Small Business Routers
(5) -
Small Business Security
(2) -
Sourcefire
(2) -
Support
(2) -
Threat Containment
(6) -
Threat Grid
(1) -
Unified Computing System (UCS)
(1) -
Voice Gateways
(1) -
VPN
(27) -
VPN and AnyConnect
(1) -
Vulnerability Management
(43) -
WAN
(7) -
Web Security
(4) -
Webex Teams
(1) -
Wired
(4) -
Wireless Security
(1)
- « Previous
- Next »
Forum Posts
I need help on how to check this error on my cisco router ISR 4331. and why it's appearing on my router logs. Thanks Apr 7 10:30:25.272: %PLATFORM-4-ELEMENT_WARNING:smand: RP/0: Committed Memory value 91% exceeds warning level 90% Version: Cisco ...
I am trying to view a specific line count of access lists on the ASA. Current if I run show access-list inside_access_in I can't specify the line I would like to filter on. I'm trying to view all hits on ACE (access list entries) on line 2. So i'm ru...
Resolved! FTD
I am trying to get better clarification on when to use which of these?FTD url object vs fqdn network object
Hi Team, Can someone please let me know why I would see Total output drops increasing on this interface. My issue is that there is a packet loss on traffic that travels via this interface. Could this be the reason? I don't have QOS enabled. SW3#sho...
I have a hub and spoke environment with a bunch of ASA 5506-X devices. I was under the impression that for a site-to-site VPN between a user (behind a residential internet connection) and my public IP hub ASA, that the private space ASA would require...
Resolved! ASA SSH to outside interface times out
Hello everyone, I did search thoroughly for this specific question and could not find an answer. I am sure it is out there somewhere but if someone here could help me out, it would be greatly appreciated. I have numerous ASA 5506-X devices in a hub-a...
Hi, I need to contact a remote LDAP server via the inside interface.this remote LDAP server is reachable via an IPsec tunnel and due to network overlapping we are natting source addresses before they passthrough the VPN.Is it possible to nat the insi...
Hi all I've got a new ASA Firepower which replaces an other old ASA. The old one has various IP Audit Policies configured, but I think for legacy reasons. What is the default today in regards to IP Audit? Is this enabled by default or not? What are...
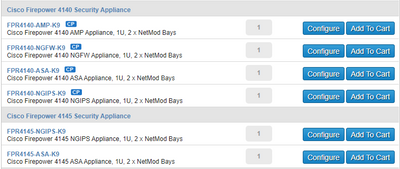
Resolved! FPR4140-NGFW-K9 vs FPR4140-NGIPS-K9
Hi I have a question about difference between the following products: FPR4140-NGFW-K9FPR4140-NGIPS-K9FPR4140-AMP-K9 I want to order the 4145 Firewall, but in "built and price" there isn't FPR4145-GFW-K9 part number.is FPR4145-NGIPS-K9 the same as FPR...
Hi Today i found out that ASA5545 CPU went to 60% and it was all consumed by the DATAPATH-0-2326 process. I could lower it to 30% by removing a capture process that wasnt removed by ASDM after the program close.The average CPU usage three days ago wa...
Hi,ASA 8.3Anyconnect users can reach INSIDE, but not DMZ. Dmz host 10.120.1.2 is what I am trying to reach.Packet-tracer shows it should be possible. Attaching my asa config.What am I missing?¨Packet-tracer:asa-kalasa# packet-tracer input vpn tcp 172...
Good day all, Currently we have deployed Cisco FMC 1600 with FTD 1020 and 2100 in HA respectively. We are running version 6.4.0.4. The FMC has been configured to sync time via NTP and is showing the correct time. The FTDs have been configured to pu...
Hy guys I have the following scenario and problem ASA 5516-XCisco Adaptive Security Appliance Software Version 9.6(1) <context>Device Manager Version 7.6(1) Escenario:I have a connection with one of our clients through VPN L2L with 2 different IPs, t...
Dears , i want to resctrict the access to VPN IPsec remote access to some public addresses .can i do that with asa ASA5512 version 9.1 ??
Learn, share, save
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
Unanswered Topics
| Subject | Author | Posted |
|---|---|---|
| 09-22-2026 04:13 PM | ||
| 08-25-2026 06:22 PM | ||
| 08-24-2026 12:26 AM | ||
| 08-20-2026 05:54 AM | ||
| 08-19-2026 07:59 AM |


New solutions
Top Solution Authors
| User | Count |
|---|---|
| 3 | |
| 2 | |
| 1 | |
| 1 | |
| 1 |


