

Resolved! old switches and ISE 3 compatibility
currently most of my switches are WS-C3560V2-48PS , do they support ISE 3 to authenticate users through 802.1X ?
currently most of my switches are WS-C3560V2-48PS , do they support ISE 3 to authenticate users through 802.1X ?
On An ISE multi-node fully distributed deployment, in a customer environment with multiple sites (more than 10) and endpoints not exceeding 2K in each site; deploying a dedicated PSN(VM appliances) on each site that will take care of sessions for tha...
Hi, Please can someone advise me on how to unlink my Primary & Secondary ISE pair so that they can be standalones?Thank you.
I have a 9200L switch with 16.9.5 software version and want to run 802.1x on a port where phone and PC are connected.The phone and PC are successful authorize on separate ports but when they are connected together, switch authorize only phone. Wiresh...
Hi Everyone, I would like to know why ISE needs the ability to change own password in AD with the Machine account. What is this functionality used for as this is flagged by a client? The ISE/AD integration lists the requirements for the Machine acco...
Hi Guys Hope all safeI just enabled Accounting on my Devices , Routers , Switches , Firewall , WLC , APshow can i trace the user's Activity's to a log file on Cisco ISE ThanksIbrahim #stayhome,StayConnected,staysafe
Hi ISE professionals,we experienced very high ISE 3.1 P1 authentication latencies (10+ seconds) at busy times during the day. However the ISE is far away from the scaling limits regarding concurrent sessions etc. This situation was so severe, that fo...
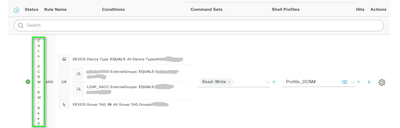
Hi Team. I don´t know why but configuring an ISE I have a problem with the size of the field "Rule Name" in my TACACS authorization rules. The problem is this field becomes too short and only shows one character while the rest of fields are very larg...
Hi,I have tried to upgrade ISE from 2.7 to 3.1, but when I do my Meraki APs can no longer connect to Radius. When I roll them back again everything works fine.Have I missed a step? Has anyone else had this issue?
Hi All,I was wondering if there are any security concern about creating a record under "Network Devices" in Cisco ISE for a network range instead of a specific /32 host IP address?It would be beneficial to configure a /16 network range, this essentia...
Hi Experts,we know that Cisco ISE is a security policy management platform that provides secure access to network resources, can we do bandwidth control by Cisco ISE policy for Wired clients (802.1x Clients) on a per user or gruop basis?
Since switching my ISE 2.7 from tradition to smart licensing, I continue to get these alerts multiple times daily. Smart Licensing Authorization Renewal SuccessSmart Licensing Authorization Renewal FailureI would like to disable these alerts but the ...
How to get the Active Directory status in the ISE External Identity Sources via the API ??I'm using the REST API below and I can see there is no users and no groups returned in the API response, but nothing about the status.https://x.x.x.x:9060/ers/...

Hi We are using ISE 2.7 and are using enforcement (closed) mode at our main office. It is working fine on all our switch C2960X-UNIVERSALK9-M), Version 15.2(2)EFor some reason the endpoints are stuck with 169.254.x.x IP. This is after the the 802.1x ...
Hi,I have a scenario where ISE controls VPN access from a ASA.Each user belongs to a certain AD group, and I want to configure different Authorization Profiles based on membership.Those profiles push dACL to the client.My question is if it's possible...
Discover and save your favorite ideas. Come back to expert answers, step-by-step guides, recent topics, and more.
New here? Get started with these tips. How to use Community New member guide
| Subject | Author | Posted |
|---|---|---|
| 10-21-2026 08:11 PM | ||
| 04-27-2026 04:44 PM | ||
| 04-22-2026 01:25 PM | ||
| 03-05-2026 07:50 AM | ||
| 02-18-2026 03:44 PM |
| User | Count |
|---|---|
| 1 | |
| 1 | |
| 1 | |
| 1 | |
| 1 |


